
DRDO has announced a standardized, secure framework for sharing its software source code with licensee industries. Unveiled at VIMARSH on September 15, the initiative aims to support software-defined defense capabilities and obsolescence management. For companies maintaining DRDO-derived systems, the practical question is how much engineering work they can perform under the resulting agreements. Ministry of Defence announcement
The opportunity is to move more maintenance work into the companies supporting the delivered system. The unresolved issue is whether the handover includes enough rights, tools and evidence to let those companies ship an accepted upgrade.
The announcement establishes the framework’s purpose and intended recipients. It does not spell out which software packages are included, what access costs, or who approves a modified version for deployment. Those details determine whether access translates into faster maintenance.
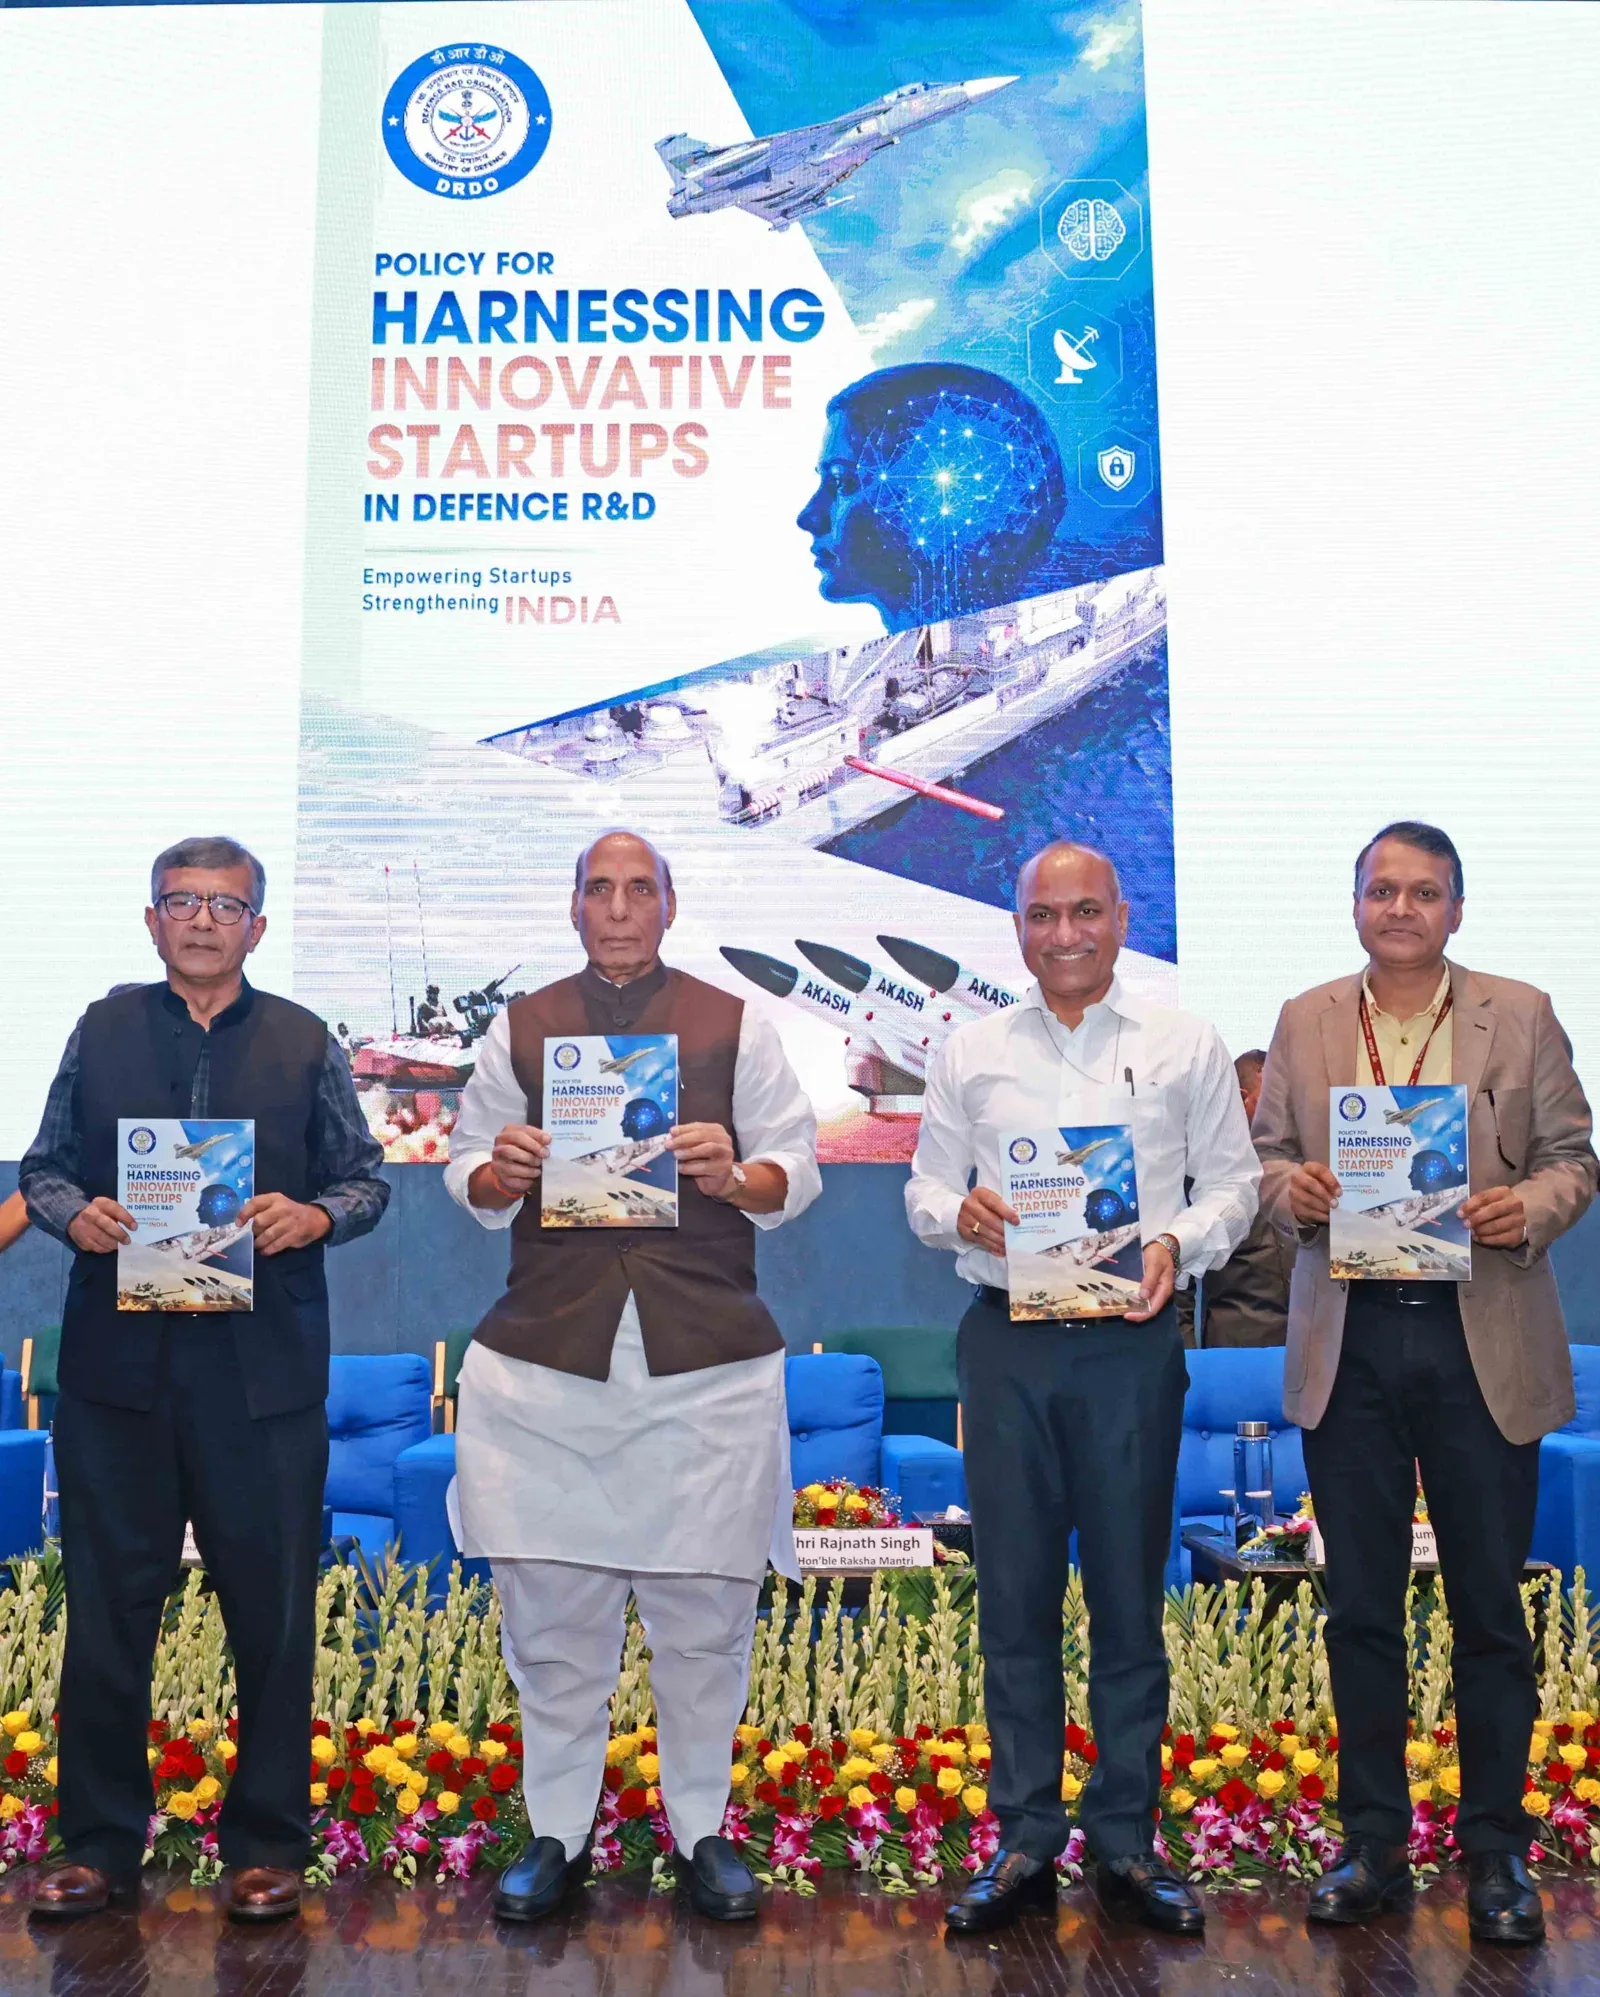
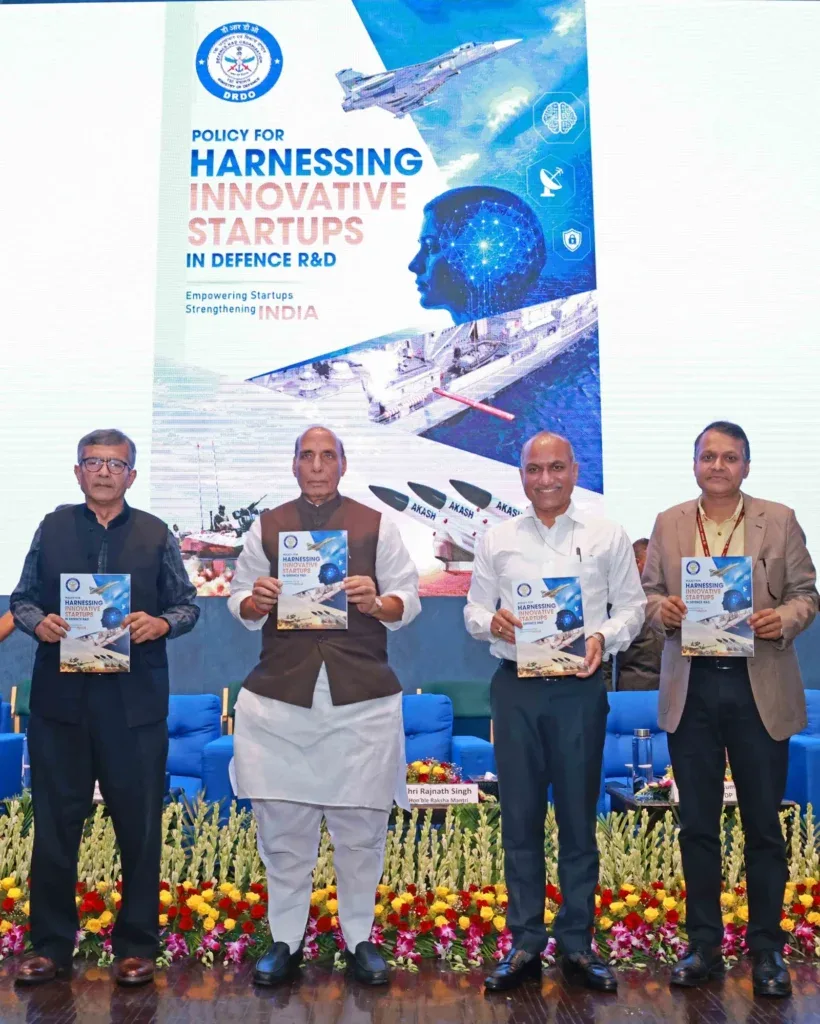
Officials present the startup-support policy at VIMARSH on September 15. This photograph documents the broader event; the visible booklet is not the source-code framework. Source: Ministry of Defence / PIB.
Source-code transfer already had a place in DRDO’s rules
DRDO’s published 2025 Procedures for Transfer of Technology already discuss source-code transfer, additional fees and conditions attached to licensing agreements. September’s announcement therefore needs to be read against an existing mechanism. Without the separate framework text, its precise procedural changes cannot be established. DRDO procedures, Annexure I to Appendix B, printed pages 38–41
The older document’s sample conditions retain DRDO’s ownership, require confidentiality and restrict redistribution. They allow modifications for internal use while disclaiming DRDO maintenance or guarantees for those modifications. These are provisions in the 2025 document; the terms of a company’s agreement under the September framework still need checking. DRDO source-code conditions
Companies should obtain the applicable framework and agreement before assuming that inspection, modification, delivery to a customer and reuse in another product carry the same permission.
The minister’s September 15 announcement on X confirms the launch and the licensee audience. It adds public provenance; it does not supply the contractual details needed to evaluate a handover.
Addressed the ‘VIMARSH’ DRDO-Industry Synergy Meet in New Delhi. Unveiled key policy initiatives to empower MSMEs & start-ups and launched framework to share software source codes with licensee industries.
— Rajnath Singh (@rajnathsingh) September 15, 2026
⁰Nine Licensing Agreements for Transfer of Technology were handed over… pic.twitter.com/fVO0uUGbSF
Where access could save engineering time
Consider a hypothetical manufacturer supporting a system whose processor has become unavailable. A replacement board might require changes to device drivers, hardware interfaces or timing behavior.
If the manufacturer receives only a compiled executable, it cannot directly edit the underlying implementation. Access to the relevant source, coupled with permission to change it, could let its engineers adapt the software and investigate faults themselves.
That is an engineering possibility, not a reported result of this policy. The work may still depend on the originating laboratory, specialist tools or approval from the system’s customer. A company cannot infer the removal of those dependencies from the announcement.
The hardware interface can also change while the application appears to run normally. A replacement driver may return data with a different timestamp, unit or update interval. The executable launching successfully would not establish that downstream software interprets those inputs correctly.
Threats and operating conditions can change too. As EyesTech’s explanation of fiber-optic FPV drones describes, moving a control path away from radio changes the assumptions behind a defensive response. Software maintenance teams need their test scenarios to reflect the system they are supporting, including cases where an old assumption no longer holds.
The same distinction applies to debugging. Seeing an implementation can help an engineer trace an unexpected result. Producing a reliable fix also requires a way to reproduce the fault and evidence that the change preserves the system’s other behavior.
The handover needs a working build
A repository is useful when the recipient can turn it into the intended executable.
A practical handover review should establish:
- The software baseline: the exact revision corresponding to the delivered system.
- The build environment: compiler versions, configuration, dependencies and any required tool licenses.
- The interfaces: hardware assumptions, message formats and external services the code depends on.
- The test evidence: expected results and a way to check changes against them.
- The release process: who reviews, accepts and authorizes a new version.
These are engineering questions for a recipient to ask. They are not confirmed requirements of the September framework.
For a reproducibility claim, the standard is stricter than a successful compilation: the same specified inputs and environment must yield identical output artifacts. The Reproducible Builds definition includes the environment and instructions alongside the source.
Pinning the source revision is only part of that job. Dependencies and build settings need a baseline as well. EyesTech’s guide to tracking versioned SDK changes explains how immutable versions and semantic differences make a software change inspectable. The same version discipline is useful here, although a defense handover may take place entirely inside an approved private environment.
A simple acceptance exercise is to have the receiving team build the agreed baseline in the approved environment and explain any differences from the reference executable. Passing that exercise would demonstrate usable build access. It would not, by itself, demonstrate that a modified system is ready for operational use.
A handover can pass inspection and still fail in use
The following is a proposed acceptance review, not a published DRDO checklist. It separates rights, engineering access and release authority so that a company can identify exactly where it remains dependent.
| Question | Evidence to request | What failure leaves unresolved |
|---|---|---|
| Can the team use the code for the agreed work? | Agreement identifying permitted uses and recipients | Possession without sufficient permission |
| Can it build the delivered baseline? | Revision, environment manifest, build instructions and reference artifacts | Dependence on an undocumented laboratory setup |
| Can it change the relevant component? | Modification rights and complete interfaces for that component | Access to files without control over the necessary layer |
| Can it demonstrate the effect of a change? | Representative test inputs, expected results and hardware access | A fix whose wider consequences remain unknown |
| Can it release an accepted version? | Named review and approval route, plus responsibility for the release | A working modification that cannot reach the customer |
| Can it recover from a failed update? | Known-good artifacts and a tested recovery procedure | A maintenance operation that risks prolonged downtime |
A company might pass the first four checks and still wait for release approval. That is why the headline benefit should be tested against the whole maintenance cycle.
For a specific upgrade, record the time spent waiting for permissions, preparing a build, implementing the change, testing it and obtaining acceptance. Some stages overlap, so the calendar delay should be measured on the actual critical path. Access to code only accelerates delivery if it shortens that path or reduces the resources consumed along it.
The business case depends on repeated maintenance
Source access can introduce an upfront engineering cost: tool setup, knowledge transfer, staff training and baseline testing. Its economic value depends on how much future work the recipient can perform more efficiently.
Consider an illustrative budget, using invented inputs rather than DRDO pricing or industry averages:
| Input | Assumed amount |
|---|---|
| Initial handover and engineering setup | ₹24 lakh |
| Cost per comparable update under the existing arrangement | ₹6 lakh |
| Cost per update handled internally | ₹2 lakh |
| Saving per update | ₹4 lakh |
On those assumptions, six comparable updates recover the setup cost: ₹24 lakh divided by ₹4 lakh equals six.
The example excludes the source-code transfer fee, recurring tool costs, financing, approval costs and changes in scope. Those costs would need to be included in a real proposal. If review and approval remain identical under both arrangements, they should appear in both estimates rather than being credited as a saving.
The arithmetic exposes a useful distinction. A manufacturer supporting many revisions may spread the setup effort over repeated work. A small company with one limited assignment may struggle to justify the same commitment. Companies should compare the cost of sustaining the capability with the workload they are actually permitted and equipped to perform.
Maintenance also brings responsibility
A company able to modify code needs a process for protecting it, reviewing changes and addressing vulnerabilities. Access can make investigation easier, but it does not automatically make the resulting software secure.
NIST’s Secure Software Development Framework offers a general reference for integrating security practices into development and for communicating expectations between purchasers and suppliers. It is useful background for evaluating a handover; it is not evidence that DRDO has adopted those requirements for this initiative. NIST SP 800-218
For a smaller company, the commercial calculation should include the people and tools needed to sustain the software. A license can become expensive to use if the recipient lacks the build environment, test infrastructure or staff required to maintain it.
Licensee access does not establish an open-source release
Open-source licensing includes rights concerning redistribution and derived works. Source-code visibility alone does not establish those rights. Open Source Initiative definition
The government announcement describes sharing with licensee industries. It provides no basis for claiming a public code release or unrestricted reuse.
The most useful next evidence would be the framework itself, followed by a documented handover: what the recipient received, which changes it was permitted to make, how those changes were accepted and whether maintenance took less time.
An informative follow-up would report the first handover against those measures: baseline build success, usable modification rights, test coverage, acceptance time and total maintenance cost. Improvements could then be attributed to a documented change rather than assumed from access alone.
For defense software companies, that is the test of the announcement’s value. The opportunity is a more workable route to maintaining licensed systems. Its scale will depend on the permissions, supporting material and responsibilities attached to each transfer.